community

FFrKeCe6

Personalized vulnerability intelligence, powered by AI

A real-time feed of trending exploits, a personalized watchlist, and an AI research agent. Powered by VulnCheck data.

Sign up for free

Sign up for free

Cogent Platform Screen - Cogent Radar

Trusted by the world’s leading security teams
Your Feed

6 NEW

3 CRITICAL

All

Critical

Watchlist

CVE-2026-09441 | Zero-Day

Palo Alto PAN-OS — Remote code execution via crafted HTTP request

Critical

CVE-2026-21345 | Active Exploitation

Fortinet FortiGate — Authentication bypass in admin interface

Critical

CVE-2026-18892 | PoC Available

Apache Struts — Path traversal in file upload handler

Critical

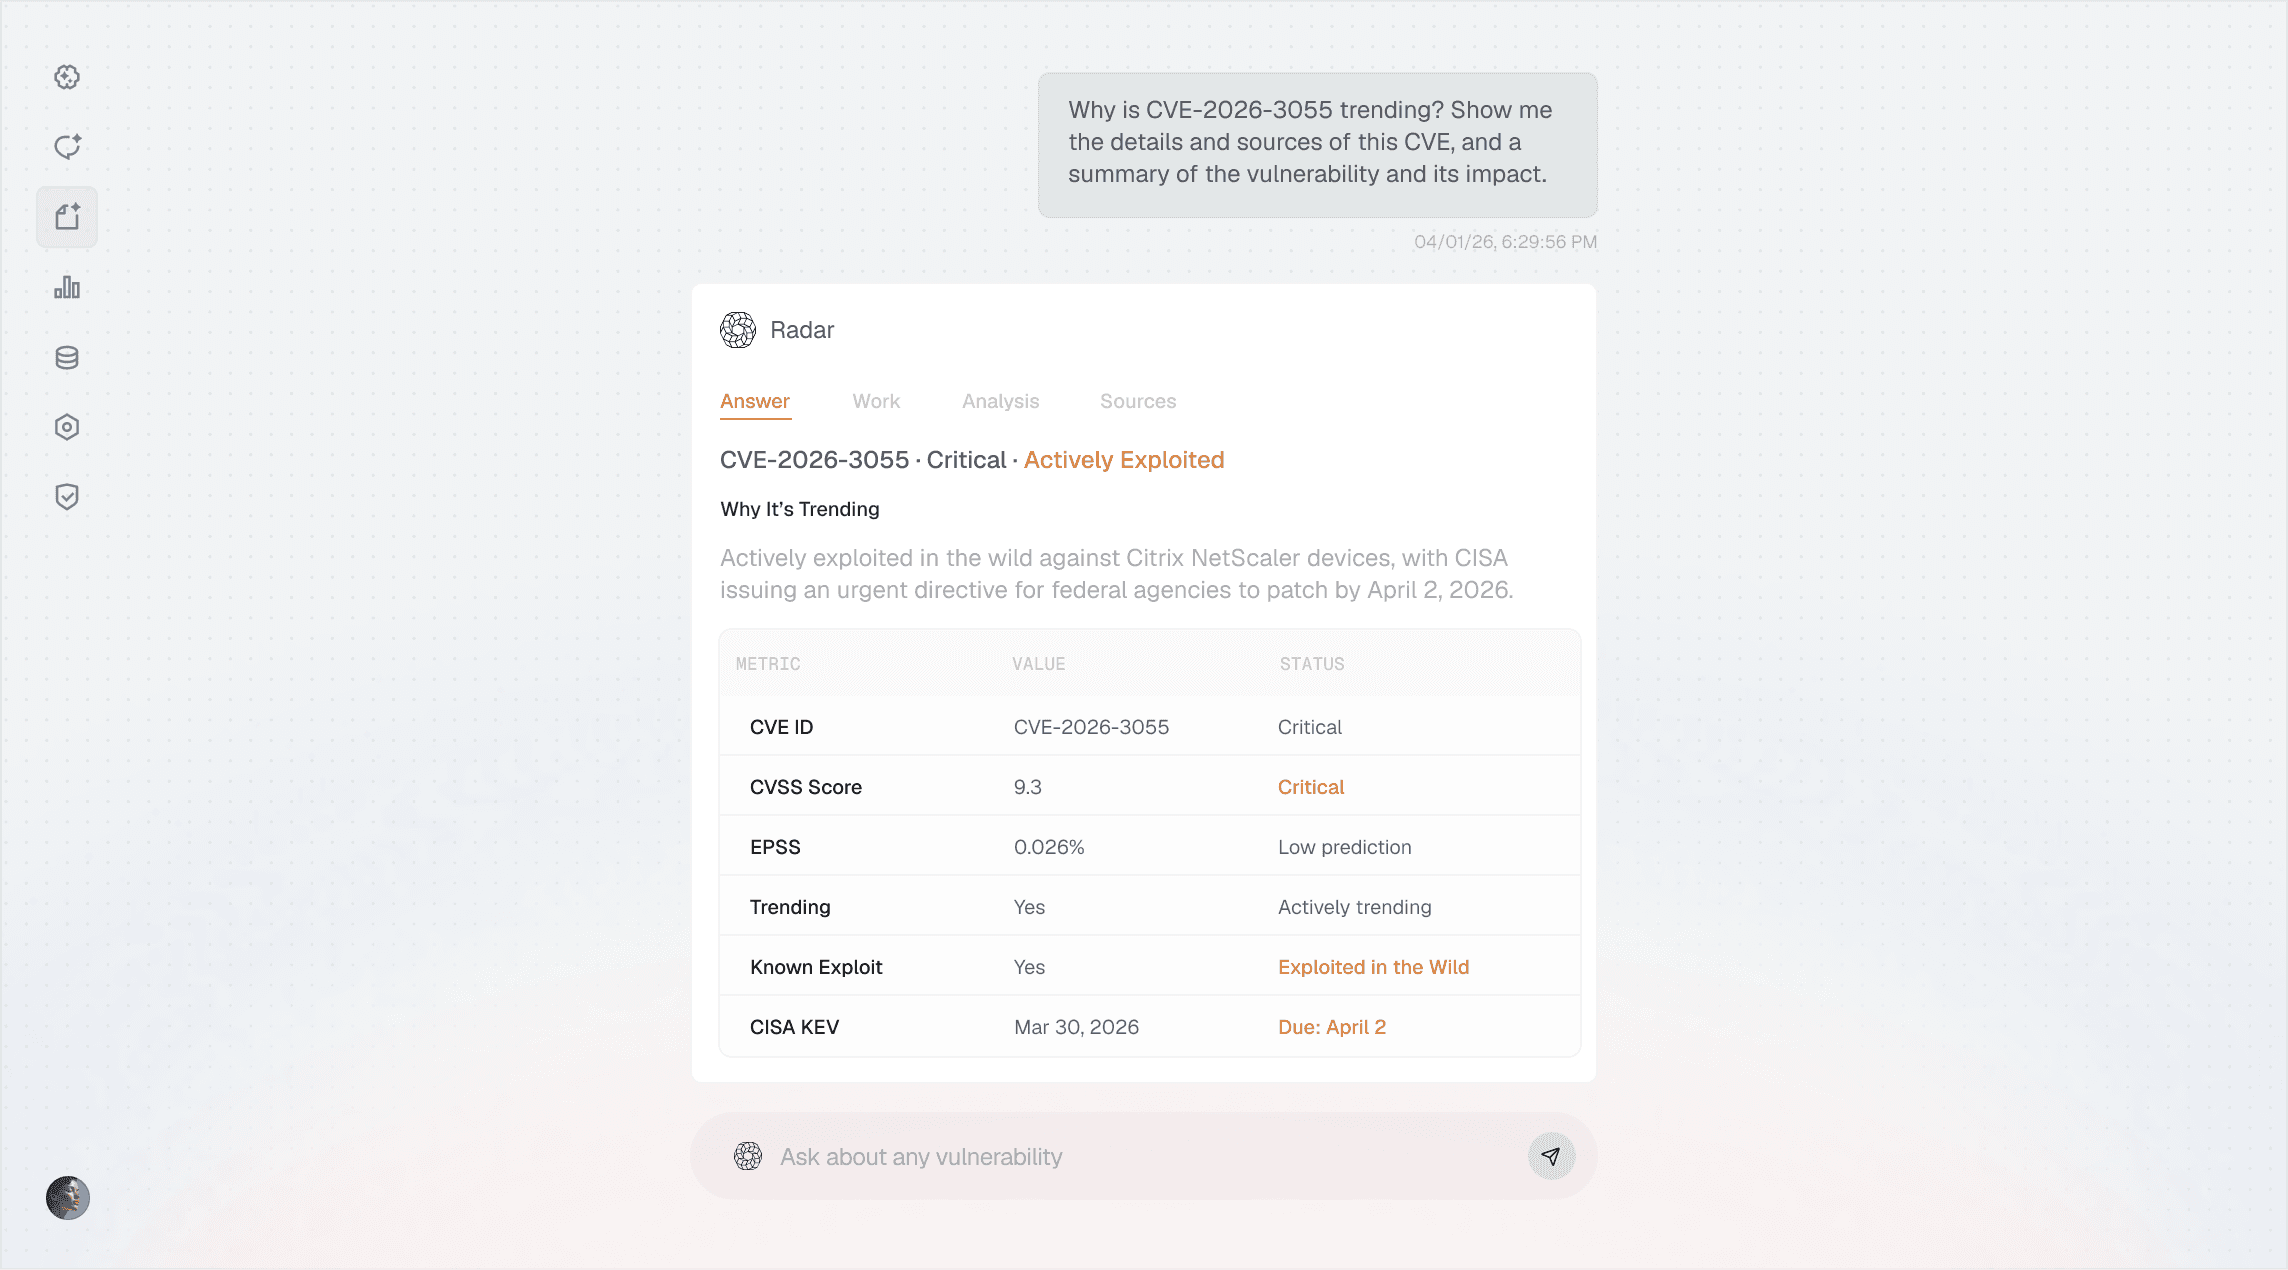
Radar

AI Research Agent

Is CVE-2024-3400 actively exploited?

Yes. It's a CVSS 10.0 command injection flaw in PAN-OS GlobalProtect, added to CISA KEV on April 12, 2024. Public PoCs exist and active exploitation across multiple campaigns is confirmed.

NVD

CISA KEV

GitHub PoCs

VulnCheck

Sources

Ask about vunerability...

Close-up of a modern glass office building exterior with partial company signage visible at the top.

7T8D%Y  R8e#lSePvWaFn%cHeB

Critical Citrix NetScaler Vulnerability Exploited in the Wild - Infosecurity Magazine

3d ago

infosecurity-magazine.com

F5 logo displayed on a black background with a red circular emblem and white lettering.

7R54%1  RGeYl6eAvJaPnEc0eG

Attackers are exploiting RCE vulnerability in BIG-IP APM systems (CVE-2025-53521

5d ago

helpnetsecurity.com

Close-up of a modern glass office building exterior with partial company signage visible at the top.

6T5%%M  RQeBlWeCvHa#n7cTeF

Critical Citrix NetScaler Vulnerability Exploited in the Wild - Infosecurity Magazine

3d ago

infosecurity-magazine.com

F5 logo displayed on a black background with a red circular emblem and white lettering.

4555%3  R5eUl0e5vGa#nJc3eP

Attackers are exploiting RCE vulnerability in BIG-IP APM systems (CVE-2025-53521

5d ago

helpnetsecurity.com

Your Feed

6 NEW

3 CRITICAL

All

Critical

Watchlist

CVE-2026-09441 | Zero-Day

Palo Alto PAN-OS — Remote code execution via crafted HTTP request

Critical

CVE-2026-21345 | Active Exploitation

Fortinet FortiGate — Authentication bypass in admin interface

Critical

CVE-2026-18892 | PoC Available

Apache Struts — Path traversal in file upload handler

Critical

Radar

AI Research Agent

Is CVE-2024-3400 actively exploited?

Yes. It's a CVSS 10.0 command injection flaw in PAN-OS GlobalProtect, added to CISA KEV on April 12, 2024. Public PoCs exist and active exploitation across multiple campaigns is confirmed.

NVD

CISA KEV

GitHub PoCs

VulnCheck

Sources

Ask about vunerability...

Close-up of a modern glass office building exterior with partial company signage visible at the top.

7A8%%$  RSe5l$eTv@aMn2cJeZ

Critical Citrix NetScaler Vulnerability Exploited in the Wild - Infosecurity Magazine

3d ago

infosecurity-magazine.com

F5 logo displayed on a black background with a red circular emblem and white lettering.

7K5A%W  R0eDlReZvMaKn0cFeY

Attackers are exploiting RCE vulnerability in BIG-IP APM systems (CVE-2025-53521

5d ago

helpnetsecurity.com

Close-up of a modern glass office building exterior with partial company signage visible at the top.

615X%I  R5eHl1eGv6aNnLcIe2

Critical Citrix NetScaler Vulnerability Exploited in the Wild - Infosecurity Magazine

3d ago

infosecurity-magazine.com

F5 logo displayed on a black background with a red circular emblem and white lettering.

4W5D%8  RReRlWeBvGaMnCc$e%

Attackers are exploiting RCE vulnerability in BIG-IP APM systems (CVE-2025-53521

5d ago

helpnetsecurity.com

Your Feed

6 NEW

3 CRITICAL

All

Critical

Watchlist

CVE-2026-09441 | Zero-Day

Palo Alto PAN-OS — Remote code execution via crafted HTTP request

Critical

CVE-2026-21345 | Active Exploitation

Fortinet FortiGate — Authentication bypass in admin interface

Critical

CVE-2026-18892 | PoC Available

Apache Struts — Path traversal in file upload handler

Critical

CCO3NBTLEJXSTM

CTO2NHT4E%XITA

C3ONNATPELX&TU

Real-time vulnerability intelligence, filtered to your stack.

Track new disclosures, trending exploits, CISA KEV and VulnCheck KEV updates, and zero-day activity across the vendors, packages, and threat actors you follow.

Radar

AI Research Agent

Is CVE-2024-3400 actively exploited?

Yes. It's a CVSS 10.0 command injection flaw in PAN-OS GlobalProtect, added to CISA KEV on April 12, 2024. Public PoCs exist and active exploitation across multiple campaigns is confirmed.

NVD

CISA KEV

GitHub PoCs

VulnCheck

Sources

Ask about vunerability...

AVIG  RIeRs$eFaTr5cShD  A7g1eJnTtM

A3IE  RKeYsZe#aGrEcPhD  AUgHeMnVtN

AXIA  RFeSsVeJaPrZc&hM  A%gBeQnWt2

Ask questions about any vulnerability in plain English.

Get clear answers with source citations in seconds. Cogent pulls from NVD, ExploitDB, GitHub PoCs, VulnCheck, CISA KEV and real-time signals to explain risk, exploitability, and next steps.

Close-up of a modern glass office building exterior with partial company signage visible at the top.

7N8H%R  RHe2lQeJvCaBnPcPeY

Critical Citrix NetScaler Vulnerability Exploited in the Wild - Infosecurity Magazine

3d ago

infosecurity-magazine.com

F5 logo displayed on a black background with a red circular emblem and white lettering.

765%%@  RXe5lReSv4a5nDcQe%

Attackers are exploiting RCE vulnerability in BIG-IP APM systems (CVE-2025-53521

5d ago

helpnetsecurity.com

Close-up of a modern glass office building exterior with partial company signage visible at the top.

695@%Z  RXeNl@eSv&aWnIc7e3

Critical Citrix NetScaler Vulnerability Exploited in the Wild - Infosecurity Magazine

3d ago

infosecurity-magazine.com

F5 logo displayed on a black background with a red circular emblem and white lettering.

4W5F%5  RMe3lLeIvMaVnUcNeX

Attackers are exploiting RCE vulnerability in BIG-IP APM systems (CVE-2025-53521

5d ago

helpnetsecurity.com

Close-up of a modern glass office building exterior with partial company signage visible at the top.

758D%T  RUe@l9e7vYa5nJcUe#

Critical Citrix NetScaler Vulnerability Exploited in the Wild - Infosecurity Magazine

3d ago

infosecurity-magazine.com

F5 logo displayed on a black background with a red circular emblem and white lettering.

7D5U%M  RAeQlLe7vAaFn8cReR

Attackers are exploiting RCE vulnerability in BIG-IP APM systems (CVE-2025-53521

5d ago

helpnetsecurity.com

Close-up of a modern glass office building exterior with partial company signage visible at the top.

6X5V%7  RHeDlUe9vDaOn7cKeV

Critical Citrix NetScaler Vulnerability Exploited in the Wild - Infosecurity Magazine

3d ago

infosecurity-magazine.com

F5 logo displayed on a black background with a red circular emblem and white lettering.

4O5P%E  R@e5l#e%vGaWn3c#e8

Attackers are exploiting RCE vulnerability in BIG-IP APM systems (CVE-2025-53521

5d ago

helpnetsecurity.com

W@aWt$cAhKlUi5s9tJ  &Y  DNaZiDl2yE  DAiUgNeVs2t3

W#aLtOcPh6l5iGs9tH  &O  DVa6iBlRyU  DFi5gRe#sPtS

W0a@tJcMhSlFiTs9tB  &C  DWaKiIlGyN  D#iSgMe1s%tC

Track what matters. Get briefed every morning.

Follow vendors, packages, threat actors, and topics. Cogent delivers a daily intelligence briefing tailored to your interests.

175%

more exploited vulns than CISA KEV

27 days

average lead over CISA alerts

ITnItJe2l9lCiCgEeVnBcJeA  S1oQu5rRc3eGs5

IEn&t#eKlAl3iSgMe5n$c@eL  SXo3uVr1c@e5sE

I$nQtBe2lElOi2g1e$n&cWeT  S&oBu&rPc5eXs9

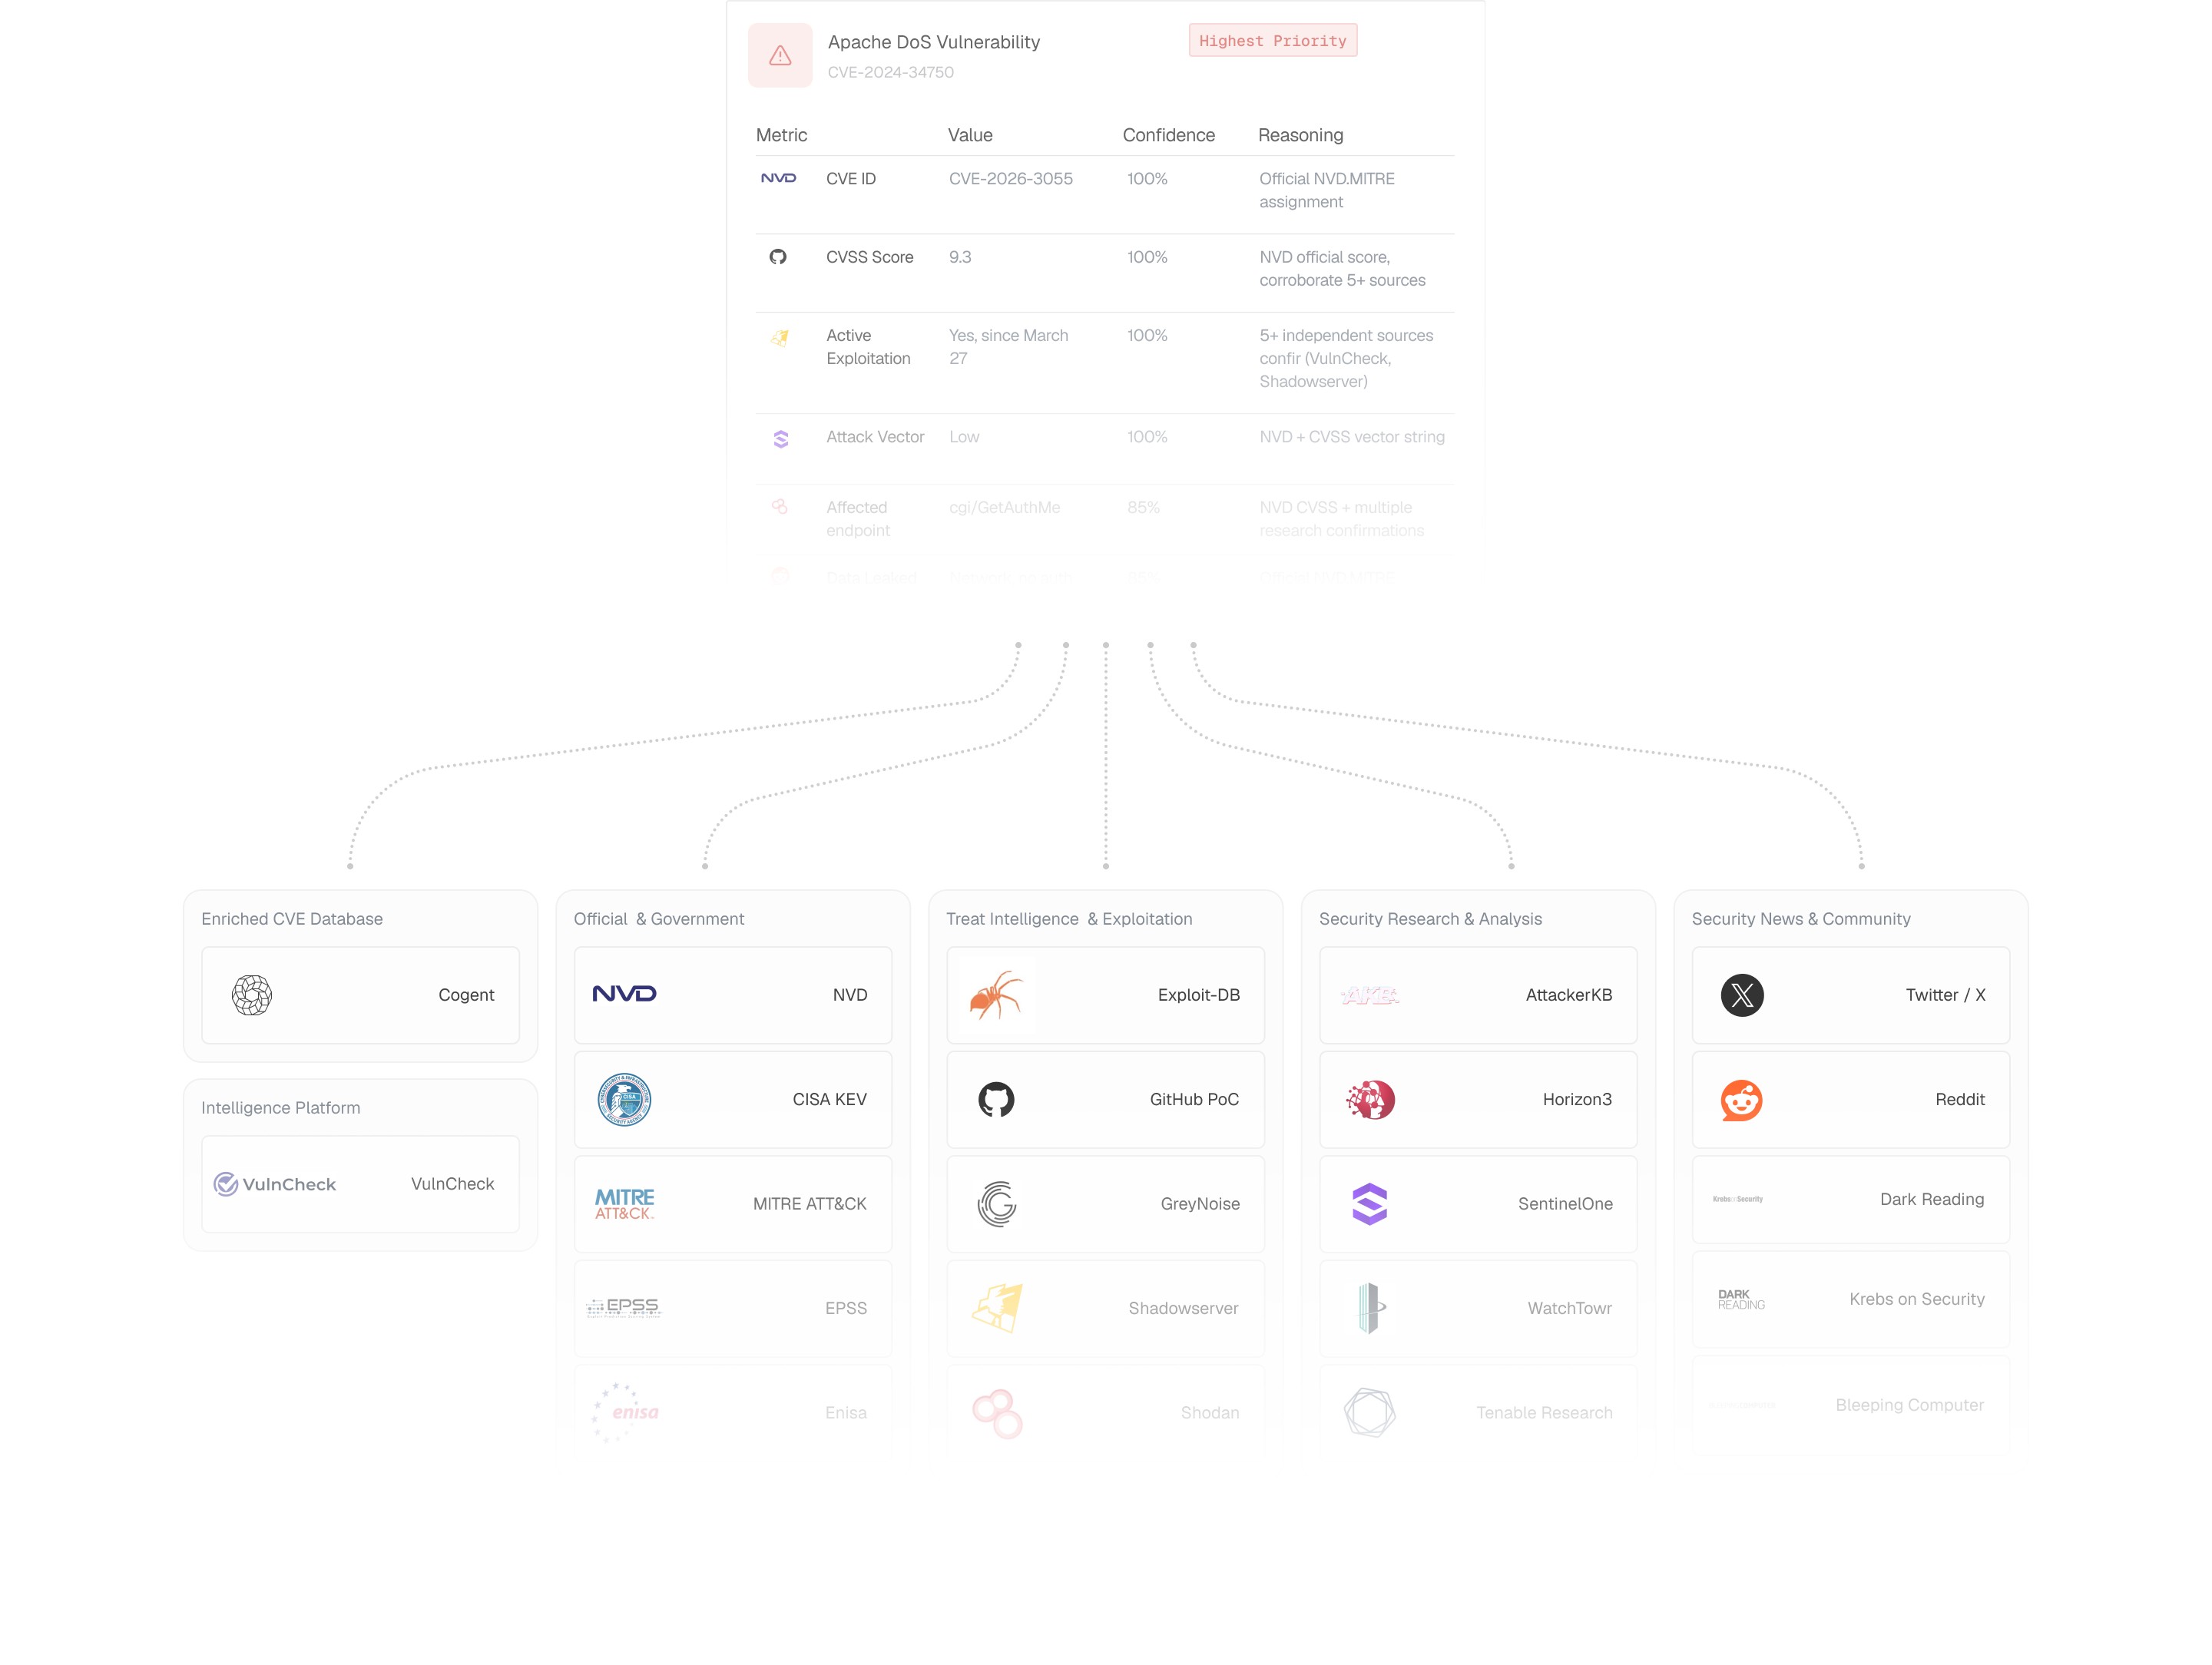
Intelligence you can trace to the source

Every data point includes a confidence score and source citation. Powered by VulnCheck, the broadest exploit intelligence catalog available.
WHh7yF  CEoJgWeMn2tQ  CPo2mVmAuFnViMtDy$

WKhHyP  C4oEgTe&n2tR  CIoWmNm8uAn7iEtOyY

W6h3yW  CGoTgVe5nYtY  CIo%m6mKuKn0i9t%y2

Your morning check-in, consolidated.

Cogent Community

Cogent Community

Typical free tools

Typical free tools

CISA Kev

CISA Kev

AI research agent

AI research agent

Cogent Radar

Yes

Yes

Typical free tools

No

No

CISA Kev

No

No

Personalized watchlist + digest

Personalized watchlist + digest

Cogent Radar

Yes

Yes

Typical free tools

Alert only

Alert only

CISA Kev

No

No

Multi-source trending view

Multi-source trending view

Cogent Radar

Yes

Yes

Typical free tools

Partial

Partial

CISA Kev

No

No

VulnCheck data (ahead of CISA)

VulnCheck data (ahead of CISA)

Cogent Radar

Yes

Yes

Typical free tools

No

No

CISA Kev

N/A

N/A

Free, no integration required

Free, no integration required

Cogent Radar

Yes

Yes

Typical free tools

Varies

Varies

CISA Kev

Yes

Yes

GBe0tR  S7tZa9r4t5e9d1

GBeHtH  SGt$a9rJtZe@dK

GXeXt1  SWtSaGr0tFeJd3

Up and running in two minutes

Sign up free

Sign up free

1

Create your free account

Gain quick and easy access. No credit card required.

2

Set your interests

Choose the vendors, packages, and threat actors you want to track.

3

Get your first briefing

Your feed starts populating immediately. Your daily digest begins tomorrow.
BMo8oPkY  aM  dAe&m8o5

See Cogent In Action

Schedule a personalized demo today to learn how Cogent can supercharge your vulnerability management program.

Book a demo

Book a demo

Free risk assessment

Free risk assessment

B6o1oJkF  a3  d1ePmToK

See Cogent In Action

Schedule a personalized demo today to learn how Cogent can supercharge your vulnerability management program.

Book a demo

Book a demo

Free risk assessment

Free risk assessment

B6o8oKk#  aK  dQe%m6o1

See Cogent In Action

Schedule a personalized demo today to learn how Cogent can supercharge your vulnerability management program.

Book a demo

Book a demo

Free risk assessment

Free risk assessment